

GDPR consulting for IT companies
How we help IT & C companies protect user data and deliver GDPR compliant solutions
- Home
- GDPR consulting for IT companies
We are happy to help
If you have any questions, please contact us!
For over 4 years we have been offering GDPR compliance services for:
Public institutions and private companies
Some of our customers are IT companies
GDPR IT Consulting
Why you and your team will enjoy working with us
GDPR services for IT companies
Our vision
At GDPR Complet, we are committed to transforming the mindset surrounding GDPR compliance worldwide. Our goal is to elevate professionalism and align our practices with international standards. We achieve this by providing the highest quality services, grounded in friendship, honesty, and integrity. We take pride in being a team of dedicated data protection professionals, striving for excellence in every aspect of our work.

Here’s how I helped them
Do you develop software or applications? Here’s what you need to know about GDPR:
Every new or existing software application must be fully GDPR compliant. The GDPR requires IT companies to protect user data and privacy.
Companies that manage the personal data of European users need to build their data protection systems and processes from the design phase onwards, develop and maintain them.
When a company decides to outsource some of its functions (eg IT outsourcing), it remains responsible for the personal data transferred to the outsourcing provider . The only way a company can avoid GDPR liability is to ensure that it cannot access personally identifiable information under any circumstances, which is often impossible in practice.
Good to know: We can help you with Data Processing Agreement (DPA) for Software Development
GDPR Consulting
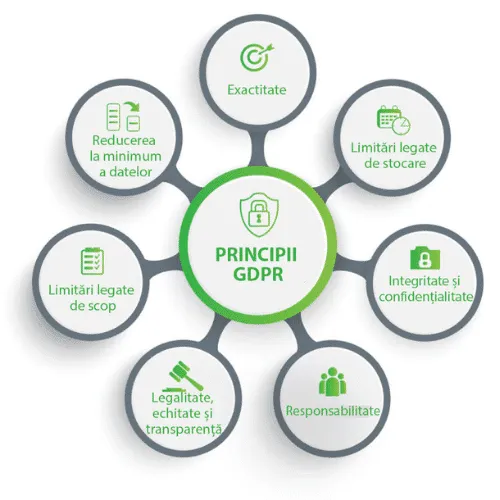
The seven key principles in GDPR that you need to keep in mind when programming and developing software solutions:
- Legality, fairness and transparency;
- Purpose limitations;
- Minimize data;
- Accuracy;
- Storage limitations;
- Integrity and confidentiality (security);
- Responsibility.
Companies need to be able to clearly describe what data they collect, for what purpose, for how long, and who can access it, among other things. It is important that you share relevant documents so that you can prove that the necessary steps for the GDPR have been completed.
We can also help you with this because we have already helped many companies that have developed websites, software platforms and mobile applications.
Although the GDPR does not require companies that collect data from EU citizens to provide their users with automated data management tools, it is in the interest of every company to do so. Without these automated personal data management capabilities, every request related to personal data (e.g. exercising the right to access personal data) should be followed by a lengthy identity verification process to prevent breach of GDPR (e.g. providing this data to others).
Here’s how I helped them
What are the key requirements for software applications which you need to keep in mind:
- Pseudonymy by default Aliases must be created for each person, and the person’s identity data must be stored in a fully partitioned area separate from other user data (for example, personal account information in an application or software platform) .
- The right to be forgotten Every EU citizen has the “right to be forgotten”, which means that, upon request, companies are obliged to give up all personal data related to a certain person. Therefore, your software or database should include tools that allow you to isolate and delete personal data as needed.
- Right to be portable According to this requirement, users must retain the ability to transfer their personal data from one service provider to another service provider. The company must configure the software to allow users to do this.
- Mandatory reporting of security incidents involving personal data The IT company must inform the affected users and the ANSPDCP (National Authority for the Supervision of Personal Data Processing) within 72 hours. Therefore, the IT company needs to detect the incidents in a very short period of time. When developing software or a mobile application, it is generally best to maximize security measures and include a security incident detection and reporting tool that can send notifications to the technical team (in real time if possible).
- Design privacy GDPR requires privacy by default, which means that the software, mobile application, or website must, by default, provide users with the highest level of security and privacy. For example, instead of automatically using a person’s name or email address as their username, the software should provide a completely random username during the account creation process.
- Informed consent Users must be allowed to provide informed consent for the collection and processing of their data. An example of informed consent applies to checkboxes when you sign up for an account on websites, software platforms, and mobile applications. In most cases, checkboxes do not need to be checked by default; the user must check them manually.
Our specialists
Get to know our amazing team
We are a dedicated team of professionals with over a decade of experience in management, law, and IT. As a trusted partner, we have established long-term relationships with more than 800 multinational corporations, SMEs, and public institutions. Our clients value our expertise in ensuring compliance with data protection laws, privacy regulations, and safeguarding personal data of employees, customers, and collaborators. By choosing us, you can confidently avoid GDPR fines and sanctions.


Media
Media appearances


